An AI agent inventory needs an operating owner, not just a name
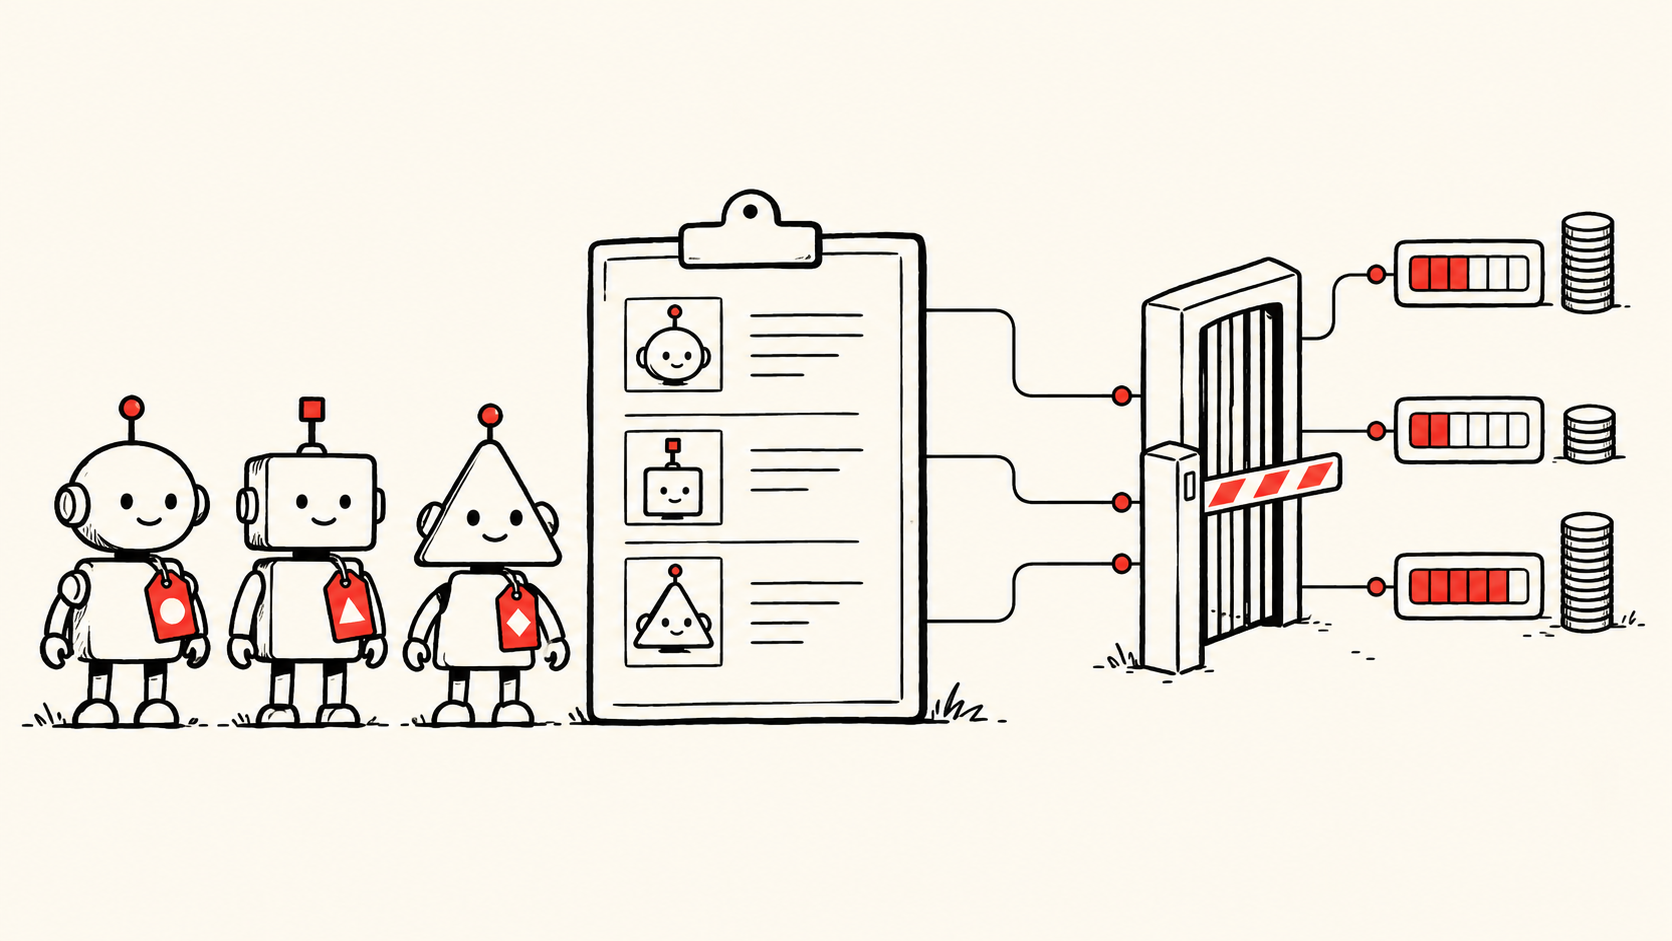
Connecting agent permissions to budget ownership can reveal risks that neither a security dashboard nor a spending report explains alone.
On October 27, 2026, AvePoint announced Trust Platform for agent governance and costs, inviting private-preview registration. These are vendor claims, not independently verified results. Issuer announcement
The interesting question is less whether enterprises need another agent dashboard than whether that dashboard can connect an action to someone able to change it. A list can identify an agent and its nominal owner while leaving unanswered who approved the workflow, which team pays for retries, and who must repair a mistaken external action. Those are different responsibilities, even when one employee's name appears beside all of them.
This article's analysis concerns that operating problem, not a product test. The following examples are hypothetical, and do not describe AvePoint customers or verified product behavior.
One workflow, several kinds of ownership
Consider a customer-support agent that retrieves order history, drafts a response and proposes a refund. The support team wants faster resolution. The platform team maintains the connector. Finance owns the refund policy. A security team approves access to customer records. Describing support as the agent's owner does not transfer all four decisions to it.
A useful inventory would therefore be a starting point for conversation rather than its conclusion. For each important workflow, the organization needs to know which person can alter the business rule, which system actually enforces it, and which evidence demonstrates the result. If these answers sit in separate tools, a common record can reduce the cost of finding them. It cannot remove disagreement about who should have authority.
NIST's AI Risk Management Framework treats inventory and accountable roles as related but distinct governance concerns. NIST AI RMF Our inference is that procurement should test the connection between them: can a named owner obtain an accurate account of an action, and can the appropriate operational team change what happens next? Counting registered agents measures neither capability by itself.
The decisive boundary is an action, not a label
In the hypothetical refund workflow, permission to read an order is not permission to issue money. Permission to propose a refund is not permission to send the customer a binding promise. A broad label such as “customer service” hides these distinctions. An evaluation that observes only whether the agent completed the task may reward the very shortcut the organization meant to prohibit.
MCP's security guidance rejects token passthrough and requires tokens to be issued for the relevant MCP server. MCP security guidance This is a concrete technical boundary, not a certification of an entire agent workflow. In our example, correct authentication still would not settle whether a particular refund complies with the company's policy.
The operational test should follow the action across systems. If a refund is blocked, can the record distinguish a policy rejection from a network failure? If the result is uncertain, will a retry duplicate the refund? If the agent is suspended, do already queued requests remain able to execute? These are evaluation questions, not allegations that a named product fails them. They require evidence from the systems that carry out the action, not just a status change in the management screen.
Cost ownership changes the incentives
The same workflow also reveals why governance and spending belong in the same discussion. A successful-looking response can be inexpensive to generate but costly to review. Conversely, an additional verification step can raise model usage while preventing manual repair. A token bill alone cannot tell a manager which change improved the operation.
The FinOps Foundation's Allocation capability links usage costs to organizational responsibility, including shared costs. FinOps Foundation Building on that distinction, we would separate the team requesting a workflow from the teams supplying its controls and recovery capacity. Otherwise a department can appear efficient by passing review and remediation work to a central team.
Imagine two versions of the support workflow. One escalates difficult cases early. The other repeatedly attempts resolution before escalating. Without counting the later human work and identifying which cases entered each route, a comparison of average AI spend would be inconclusive. No numerical saving follows from this example; it shows why the measurement boundary matters.
There is a genuine counterargument to fine-grained attribution. Recording every minor call can impose more administrative effort than it saves, and shared infrastructure cannot always be divided fairly. A practical approach is to start with costly or consequential workflows, disclose the allocation rule, and retain an explicit category for shared overhead. False precision is not better accountability.
What a platform can, and cannot, settle
A unified system could make these relationships easier to inspect and reduce duplicated evidence gathering. It could also become an additional dependency: incomplete connectors, inconsistent identifiers or delayed events could make its picture appear more complete than it is. Neither outcome is established by a launch announcement.
A serious trial would ask the business owner, security reviewer and budget holder to explain the same sample of completed and failed work. Agreement should cover not only what the agent attempted, but which rule applied, where enforcement happened and who absorbed the resulting cost. Disagreements are useful findings, not cosmetic defects to hide before a demonstration.
The relevant purchasing question is therefore whether the platform helps the organization make and verify those decisions. The number of agents discovered is useful coverage information. It becomes evidence of better governance only when the organization can connect that coverage to understandable authority, observable outcomes and a defensible account of the work required to operate safely.
Information only. No investment, legal, tax, or financial advice.